
For banks, PSPs, exchanges and institutions
The Business plan, plus what your risk committee asks about
Deployment in your environment, contractual SLA, a named team, and a joint review with your compliance people before any contract is signed.
Share the Trust, Guard the Keys
The questions that decide an enterprise deal are never on the feature grid
By the time a bank, PSP or exchange reaches procurement, the feature comparison is settled and the conversation is about deployment, key custody, exit and evidence. Those are contract and architecture questions, and the Business plan does not answer them — a negotiated Enterprise agreement does.
- Where does the co-signer runYour MPC party can run in your own cloud or data centre as a self-hosted co-signer, reached over your network on your schedule.
- What happens if we leaveYour backup unwraps with your RSA key in a public offline tool. Exit does not depend on our cooperation, our uptime or our goodwill.
- Who can approve what, provablyRoles, quorums and approval-gated administration — with the evidence a second-line reviewer can read without asking us for a screenshot.
What the contract adds
Everything in Business is the baseline; these are the Enterprise deltas.
Dedicated, self-hosted or VPC — including the server co-signer as a binary on your own infrastructure (Docker or Helm, Postgres or cloud-object persistence).
Contractual uptime and response-time commitments defined per agreement — not a marketing badge.
A team that knows your deployment by name, around the clock.
Accounts, volume, seats, invoicing and billing terms — negotiated, from $1,999/mo.
Joint session with your risk and compliance teams as step one of onboarding — not a favour, the process.
Structured migration from your current vendor: new 3-of-3 keys, on-chain moves, parallel running until you cut over.
Compliance posture, stated plainly
Including the answers that are deliberately "no" — your diligence deserves the real picture.
| Item | Status |
|---|---|
| SOC 2 Type I / Type II | In progress |
| ISO 27001 | In progress |
| Independent security audit | In progress |
| GDPR | Compliant |
| Non-custodial architecture | By design — 3-of-3 signing, client share mandatory at every signature |
| Qualified custodian status | Deliberately no — you remain custodian of record; if your regulator requires a qualified custodian, we will say so honestly |
How onboarding runs
Three steps, risk team first.
1 · Scope with your risk team
Architecture review and the compliance questionnaire before any commercial conversation. The 3-of-3 signing model — with an open-source recovery path your auditors can read — tends to shorten this step considerably.
- ✓Deployment model decided here: SaaS, dedicated, self-hosted, VPC
- ✓Key ceremony and recovery procedures walked through end-to-end
2 · Pilot on testnet
Your engineers integrate against real endpoints under a standard account. Wallet creation, policy setup, webhook flows and co-signer deployment are all testable before a single mainnet transaction.
- ✓Same API surface as production
- ✓Server co-signer deployable in your environment during the pilot
3 · Contract and go-live
SLA, volumes and deployment fixed in the agreement; a named team owns your account from day one. Migration from an incumbent vendor runs in parallel until you cut over.
- ✓Contractual SLA with response-time commitments
- ✓Named 24/7 team, direct channel
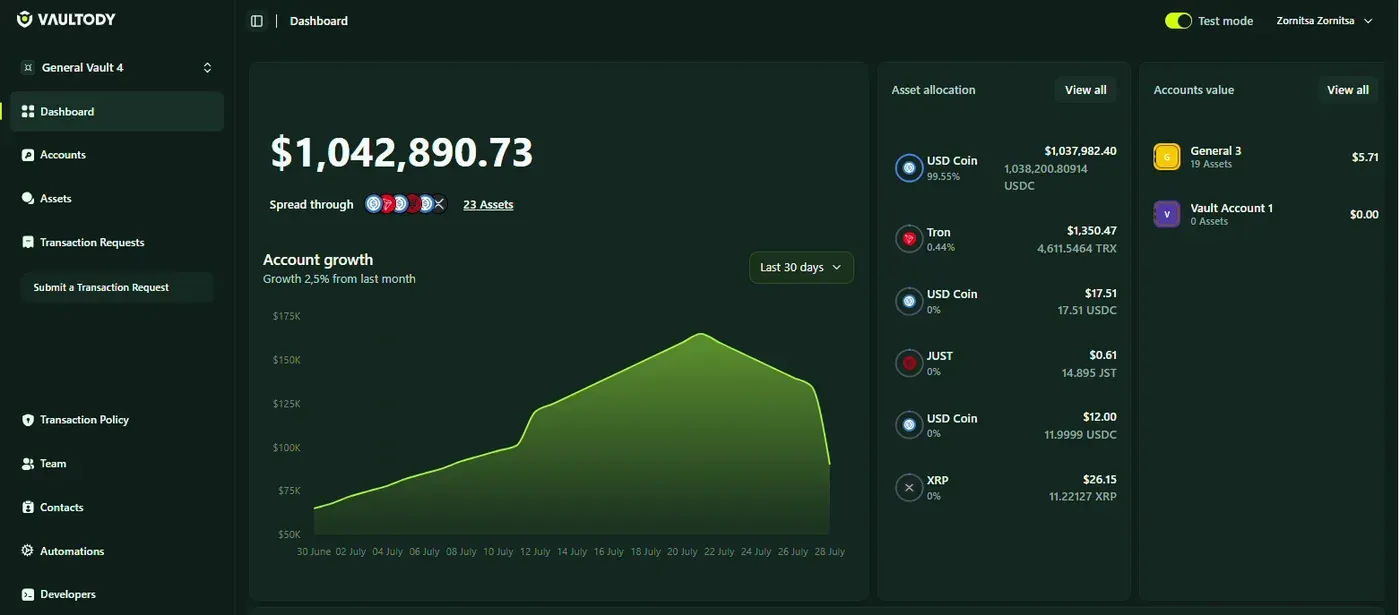
What the Enterprise agreement adds
Everything in Business is the baseline; these are the Enterprise deltas.
How onboarding runs
Three steps, and none of them start on mainnet.
Architecture review and the compliance questionnaire before any commercial conversation. Deployment model, key-ceremony procedure and recovery path walked end to end.
Your engineers integrate against real endpoints under a standard account. Policy setup, webhook flows and co-signer deployment are all testable before a single mainnet transaction.
The production committee is generated with your party present. Addresses are derived, the backup ceremony completes, and only then do funds move.
Move flow chain by chain while the old rail stays up. Reshare lets you change parties later without changing an address.
Who signs an Enterprise agreement
Institutions that must keep custody in-house and need the key material to prove it, with an auditable exit and a deployment their own security team controls.
PSPs, exchanges and OTC desks where volume commercials and fee mechanics — TRON energy, gas sponsorship, batch payouts — decide the unit economics.
Funds and asset managers that answer to LPs and auditors: quorum on movement, exportable evidence, and no third party that can move a position.
What we will not claim in a procurement pack
Vaultody is co-signing infrastructure. If your mandate requires a licensed custodian of record, that is a different vendor category.
There is no pooled honeypot to insure — your party is mandatory. Ask us for the architecture argument, not a policy certificate.
SOC 2 and ISO 27001 are under way and we date them honestly in diligence rather than implying a badge we have not earned yet.
Our uptime does not decide whether you can sign — yours does too. Plan a server co-signer for continuity.
Frequently asked questions
Get answers to commonly asked questions.
Can we run Vaultody entirely in our own environment?
The server co-signer always can — it is a binary you self-host. Dedicated and VPC deployment of the broader platform is an Enterprise option scoped in the architecture review.
What does the SLA actually cover?
Contractual uptime and response-time commitments, defined per agreement — the terms are in the contract, not on a slide.
Are you a qualified custodian?
Deliberately no. Vaultody is non-custodial infrastructure — you remain custodian of record. If your regulatory position requires a qualified custodian, we will tell you honestly and you should look at that category.
Where does compliance stand right now?
SOC 2 Type I & II, ISO 27001 and an independent security audit are all in progress; GDPR compliant today. We publish statuses plainly rather than badge-dropping.
Share the Trust Guard the Keys
Bring your risk team — the architecture holds up to scrutiny.